

Trading
Explore a wide range of markets with competitive pricing, deep liquidity, and advanced trading tools.
Learn More 
Platform
Trade seamlessly with TMGM's powerful platform, built for speed, precision, and a superior trading experience.
Learn More Trading Platform
Academy
Learn the fundamentals of trading with beginner-friendly resources, including guides, webinars, and market insights.
Learn More News & Analysis
Get real-time market updates and expert analysis to stay ahead of trading opportunities
Learn More News & Analysis
About
Learn what sets TMGM apart — our global presence, regulatory strength, and commitment to innovation in trading.
Learn More Why Choose TMGM
Sponsorship
Why is Bitcoin's quantum countdown accelerating as estimates continue to fall?
For Bitcoin (BTC) and the wider cryptocurrency market, the threat from Artificial Intelligence (AI) and quantum computing now hinges on when hardware catches up, rather than whether it will.
Neither technology can independently break Bitcoin’s cryptography today. Even so, progress in AI-assisted research is giving the quantum computing threat a new dimension.
The gap is nevertheless narrowing as AI and quantum computing advance, at a pace faster than anyone had anticipated before 2026.
For more than a decade, blockchain functioned as a trustless ledger regarded as mathematically unbreakable. Underpinning Bitcoin’s security was a problem too complex for any classical computer ever built to solve.
The problem in question is the Elliptic Curve Discrete Logarithm Problem (ECDLP-256); it forms the mathematical barrier between a crypto wallet’s public key and its private key.
Despite five years of AI advances that threaten Bitcoin’s underlying security, solving this long-standing mathematical problem remains computationally infeasible for classical computers. That qualification matters, but it leaves an uncomfortable question: how much longer will this hold?
Why does 6M Bitcoin define the stakes?
Quantum Alliance estimates that wallets with public keys already exposed and visible on the blockchain hold approximately 6.4 million Bitcoin, or 32.2% of the entire circulating supply. The nine-member coalition was launched in October 2026. Its estimate includes Satoshi Nakamoto’s 1.1 million BTC, while an even larger figure of 6.9 million BTC is cited by the European Supervisory Authorities (ESAs).
The financial exposure is far from theoretical. With Bitcoin trading near $82,000, these holdings are worth upwards of $566 billion at current market prices, despite their continuing structural vulnerability.
A September report from institutions under the ESAs warned that quantum computing could undermine some cryptographic networks securing transactions, blockchains, databases and communications even before becoming commercially viable. According to a CoinDesk article, the report did not specify when commercial viability might be reached.
Where does the quantum threat come from?
Bitcoin and other cryptocurrencies face quantum risk because of cryptography’s early architecture. Wallets with pay-to-public-key (P2PK) outputs, the default format in Bitcoin’s early days, published their public keys directly on-chain with each transaction. Address reuse also exposes public keys. Once visible, these keys become targets, including those associated with the 1.1 million BTC attributed to Satoshi Nakamoto. Those coins remain dormant in the original P2PK addresses, which have seen no activity for more than 15 years.
There is, however, no immediate danger to Bitcoin held in P2PK addresses: no existing computer can solve the ECDLP-256 mathematical problem. The risk lies ahead. Debate therefore centres on how distant that point is and whether someone could bring it closer.
A different prospect arises with a quantum computer using Shor’s algorithm: it could solve ECDLP-256 exponentially faster than any classical computer.
In March, Google brought forward substantially its deadline for readiness ahead of Q-Day, when current quantum computers could solve ECDLP-256 and break public-key cryptography algorithms. The company identified 2029 as its preparation deadline and urged the rest of the world to follow suit by beginning to implement post-quantum cryptography (PQC) algorithms that supplement or replace elliptic curves and RSA.
In the post, Google’s VP of security engineering Heather Adkins and senior cryptography engineer Sophie Schmieg stated: “As a pioneer in both quantum and PQC, it’s our responsibility to lead by example and share an ambitious timeline. By doing this, we hope to provide the clarity and urgency needed to accelerate digital transitions not only for Google, but also across the industry.”
To put this in perspective, Google said that breaking ECDLP-256 now requires fewer than 500,000 physical qubits, having lowered its estimate by a factor of 20. By comparison, Willow, the company’s most advanced chip, has 105 qubits.
The concern extends beyond Google. Earlier in 2026, other organisations also predicted an earlier-than-expected Q-Day, among them Oratomic, a start-up linked to Caltech.
For Richard Carback, CTO at Postquant Labs and a founding member of the Quantum Alliance, 2028 is a very real possibility for a cryptographically relevant quantum computer. Bryn Bennett, CRO at The Vault, offers no specific date, framing the issue instead as an operational challenge rather than a theoretical one.
Speaking at the Quantum Alliance launch in October, Bennett said, “Nobody knows the date, but the estimates keep falling, and the risk is one we can already plan for,” and added, “The question for custodians isn't whether the date is 2028 or 2035; it's whether you can migrate in time if it arrives early.”
How is AI bringing Q-Day closer?
AI’s entry changes the quantum computing landscape and its outlook substantially. Until recently, the prevailing view was that quantum hardware development remained the critical constraint: increasing the number of qubits requires time, capital and engineering.
That obstacle remains, but AI has added another dimension to the risk. It can reduce the algorithmic cost of attacks independently of advances in quantum hardware.
Eigen Labs launched ECDSA.fail in March, challenging researchers to design the most computationally efficient quantum circuit for breaking the cryptography that protects Bitcoin and Ethereum. More than 100 participants joined within the first eight weeks, collaborating with AI coding agents such as OpenAI’s GPT 5.6 and Anthropic’s Claude Opus 5. Their more than 400 circuit submissions brought the spacetime cost down by about 86%, from a baseline of 10.75 billion Toffoli-qubits to 1.496 billion.
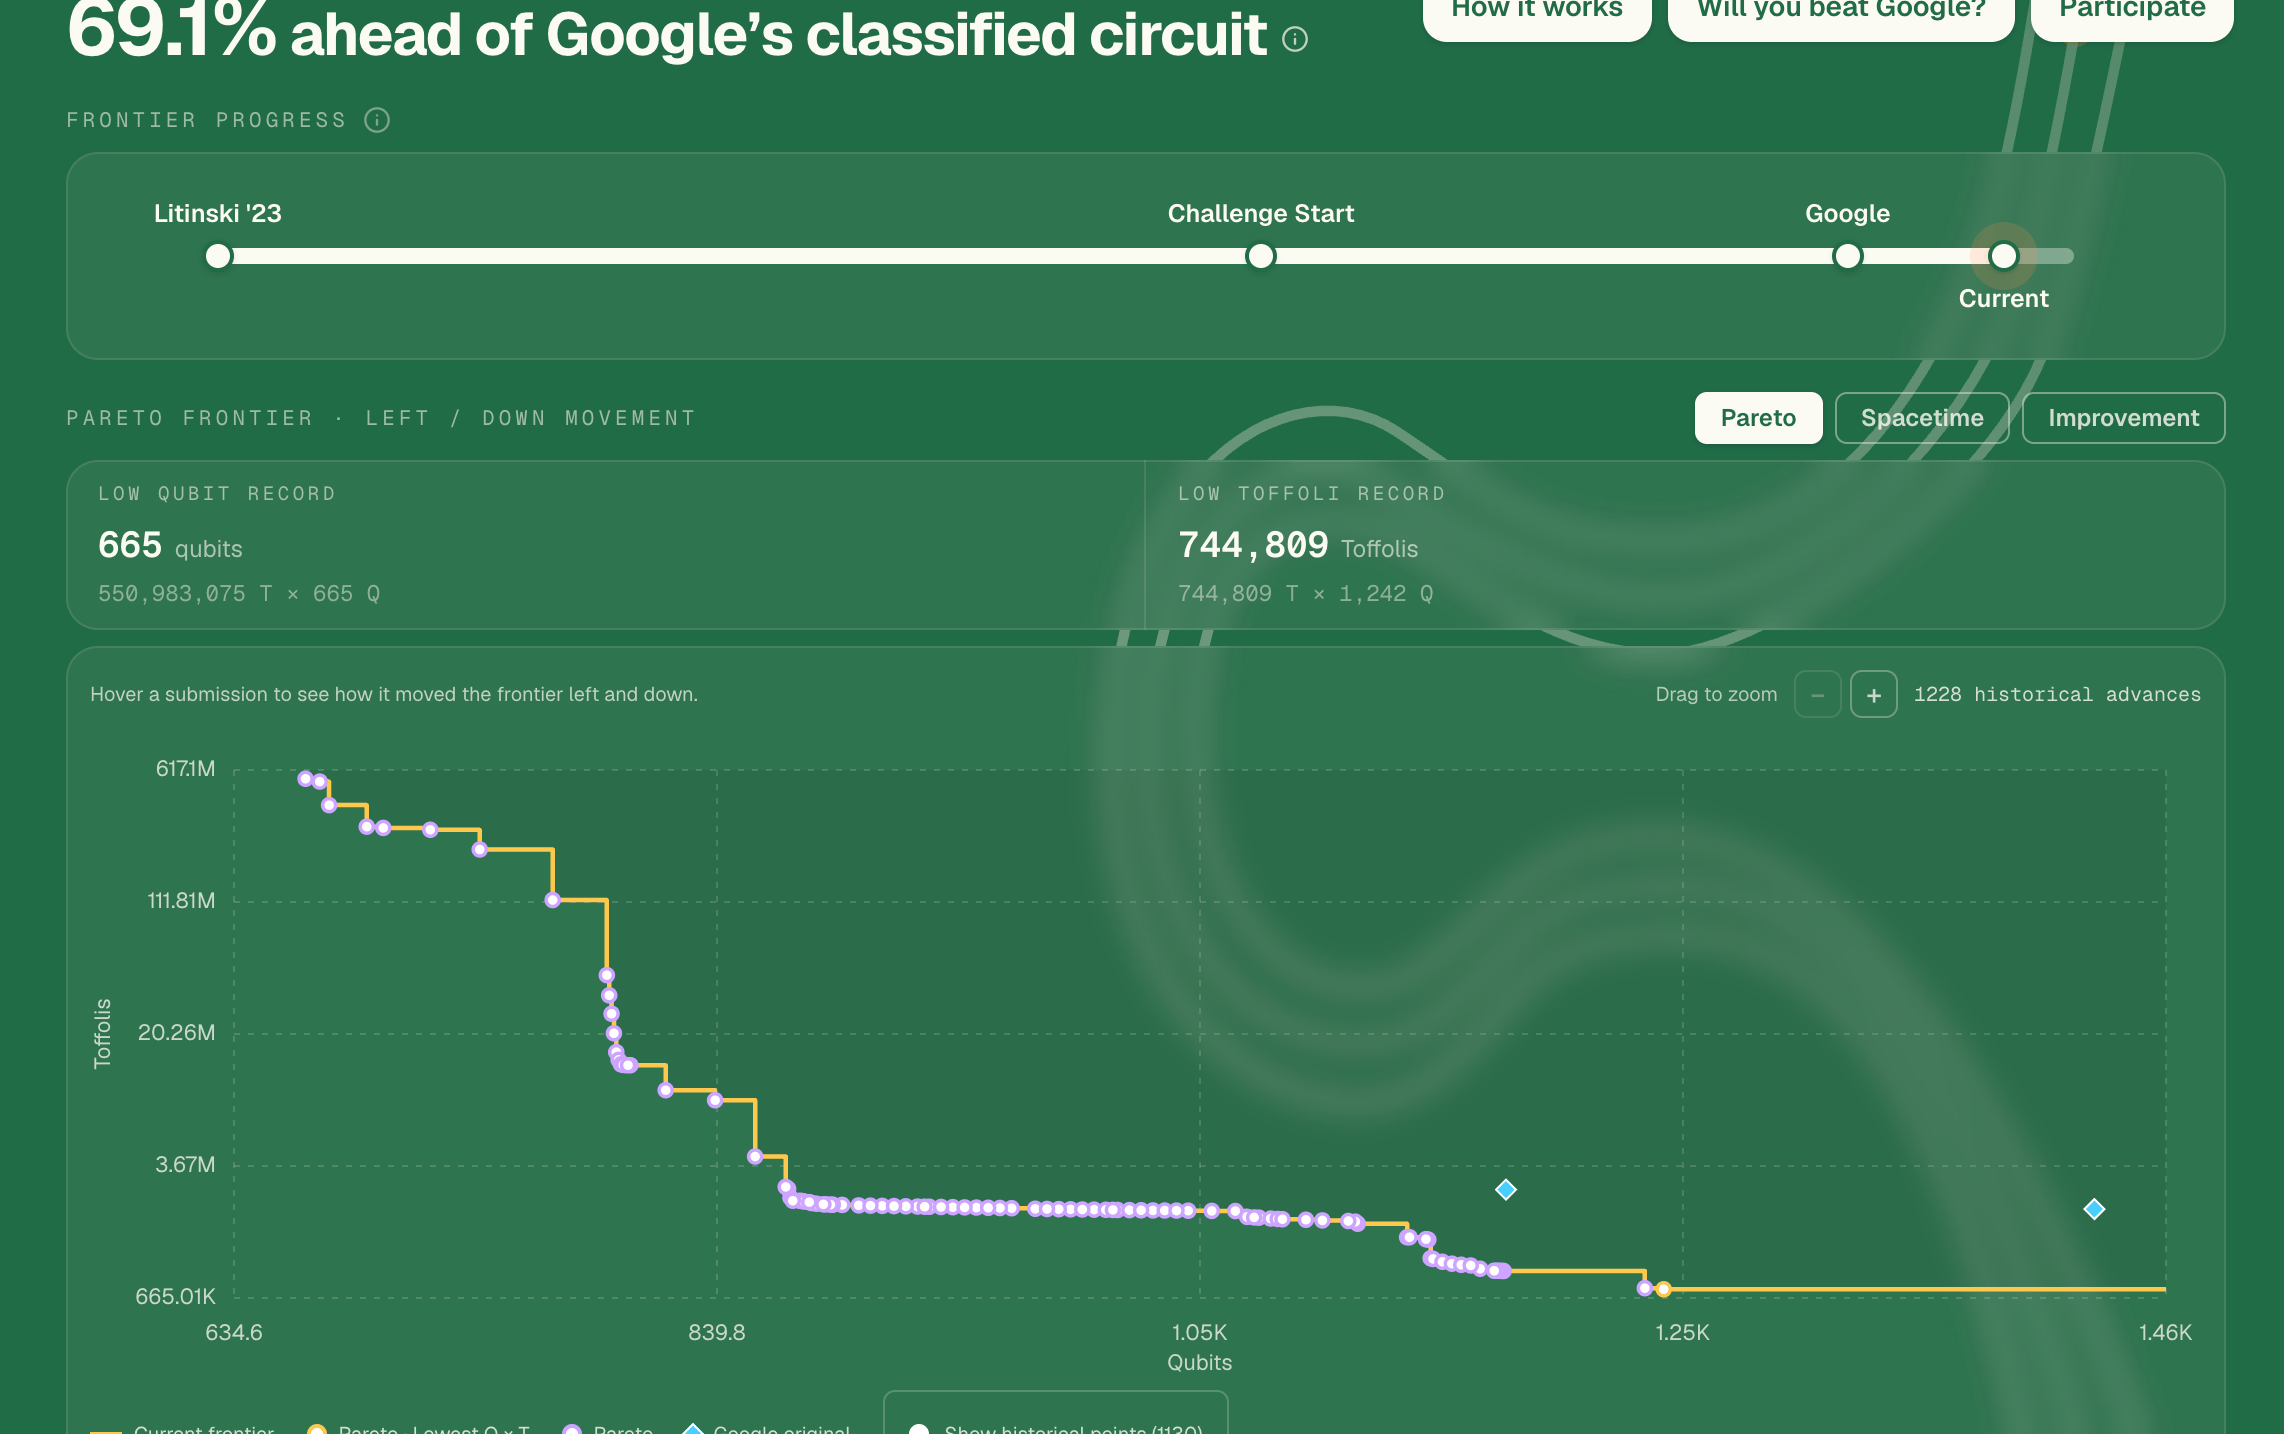
The researchers described the process as follows: “Beyond the resulting circuits, ECDSA.Fail provides a case study of Open Autoresearch: a verifier-gated research process in which human participants and AI agents iteratively generate, implement, test, and share candidate improvements against a common measurable objective,”
The race towards Q-Day also involves organisations and open-source communities beyond Eigen Labs’ ECDSA.fail. Among them is Double AI, whose autonomous AI system WarpSpeed generated a circuit with 2.5 times the spacetime efficiency of Google’s original design.
AI does not threaten Bitcoin through quantum hardware itself, nor can it break the cryptography today. Its significance is that it may reduce the hardware threshold required for a successful attack.
Rather than advancing on separate tracks, AI and quantum computing are reinforcing each other as their threats move towards convergence.
Can stakeholders reach consensus on the crisis?
Mitigation efforts are already being explored by blockchain stakeholders, including Bitcoin’s Pay-to-Public-Key-Hash (P2PKH). By hiding the recipient’s public key behind a hash, this technology offers partial protection, according to Fireblocks.
Improving cryptographic security over the longer term requires a solution to the ECDSA problem. Proposals for several soft fork changes are now being debated.
Uncertainty over when Q-Day will arrive is nonetheless slowing post-quantum cryptography migration. Discussions focus on algorithm selection, governance and the difficulties of upgrading decentralised networks.
Replacing the digital signatures behind every Bitcoin transaction is essential to a successful quantum migration. Developers, miners, wallet providers, exchanges and millions of users would need to reach broad agreement on a new cryptographic standard, a coordinated migration schedule and an approach to dormant coins.
Experts nevertheless consider migration achievable before quantum computing becomes a threat to Bitcoin and other blockchain protocols. In a recent YouTube video, Bitcoin.com said the industry can expect native support for post-quantum signatures, the replacement or strengthening of weakened primitives, or more robust consensus mechanisms.
What are the key points for Bitcoin holders?
Treating the issue as a choice between Bitcoin being entirely secure and already compromised misses the point. Both extremes are mistaken and carry risks; the reality is more nuanced and often uncomfortable.
Bitcoin is not being stolen from you now, but there is less room for complacency. The threat from AI and quantum computing is real, credible and well documented. It is not materialising today, since no existing computer can break elliptic curve cryptography. Still, Q-Day is approaching faster than anyone had anticipated before 2026.
The exposure of 6.4 million Bitcoin represents a structural weakness rather than a software flaw. Public keys for these wallets are permanently visible on the blockchain, providing precisely the data that a quantum attacker would require. Moving to a quantum-resistant address format is the only solution, and this migration should take place before Q-Day.
Although AI and quantum computing present distinct threats, their combined effect creates the same problem.
There is no precise timeline or confirmed date for Q-Day. However, most organisations, Google included, identify 2028-2031 as the most likely consensus window.
Available solutions remain incomplete.
Governance and consensus pose the greater challenge, exceeding even the technical threat. Migration requires every stakeholder across a decentralised global network to agree on an approach, coordinate and carry it out.
Holders can act now by refraining from address reuse, which reveals public keys. Move holdings from P2PK outputs into P2PKH, P2WPKH, or Taproot addresses
The bottom line: Quantum risk is genuine, but AI’s reinforcing effect and the unresolved outcome make it an even more nuanced issue.
FAQs on Bitcoin, altcoins and stablecoins
The largest cryptocurrency by market capitalisation, Bitcoin is a virtual currency created to function as money. No single person, group or entity can control this payment method, removing the requirement for third-party involvement in financial transactions.
Any cryptocurrency other than Bitcoin is generally classed as an altcoin. Some, however, exclude Ethereum as well, arguing that forks originate from these two cryptocurrencies. Under that interpretation, Litecoin is the first altcoin: it was forked from the Bitcoin protocol and is therefore an “improved” version of it.
Designed to maintain a stable price, stablecoins are cryptocurrencies backed by reserves of the assets they represent. Each stablecoin’s value is pegged to a commodity or financial instrument, such as the US Dollar (USD), while an algorithm or demand regulates its supply. Their primary purpose is to give investors a route into and out of cryptocurrency trading and investment. They also offer a way to store value, given the volatility generally associated with cryptocurrencies.
Measured as Bitcoin’s market capitalisation divided by the combined market capitalisation of all cryptocurrencies, Bitcoin dominance indicates the level of investor interest in Bitcoin. BTC dominance is typically high ahead of and during a bull run, when investors favour a relatively stable cryptocurrency with a large market capitalisation, such as Bitcoin. Falling BTC dominance generally signals a shift of capital and/or profits into altcoins in pursuit of higher returns, often setting off a surge in altcoin rallies.
POPULAR ARTICLES
1Why is 1.1000 in focus for the Euro as France's bond spreads stand close to the 2011 crisis record?2European Central Bank: Do rising bond yields strengthen the case for an October hold? – ING3Stronger Fed rate hike bets drive silver down 5% to three-month low4Bank of England: Firm UK inflation brings November hike into forecast – Danske Bank5South African Rand: SAGBs find support in fiscal discipline – Societe Generale6Canadian Dollar holds steady as US Dollar rebound caps further gains7Why is Bitcoin's quantum countdown accelerating as estimates continue to fall?8Mexican Peso: How are Banxico risks pressuring MXN against the US Dollar? - Commerzbank9Euro: Could French spreads drive losses against US Dollar? – BBH
LIVE QUOTES


ALL ABOUT CRYPTO
Crypto Trading Hours: Best Time to Trade Crypto
Is Crypto Trading Legal in India? A guide for Indian Traders
How to Trade Cryptocurrency? The Best Beginner’s Guide
Trading Cryptocurrencies Using CFDs
Understanding Ethereum: More Than Just Another Cryptocurrency
5 Essential Cryptocurrency Trading Strategies Every Trader Should Know
Blockchain Fundamentals: Definition and Significance
Day Trading Cryptocurrency: A Beginner’s Guide to Getting Started
What is Bitcoin Halving & When is the Next Halving
Get Started!
Sign up and access the Global Markets in less than 3 minutes

Connect With Us









Contacts
Phone: +61 2 8036 8388
Fax: +61 2 8036 8388
Email: support@tmgm.com



The information provided on this website is of a general nature only and does not constitute personal financial advice. Before acting on any information on this website, you should consider the suitability of the information in relation to your objectives, financial situation and needs. Investing in CFDs and FX Margin Contracts carries significant risks and is not suitable for all investors. You may lose more than your initial deposit. You do not own, or have, any interest in the underlying asset. We recommend that you seek independent advice and ensure you fully understand the risks involved before trading. It is important that you read and consider the disclosure document before you acquire any product listed on the website. The information and advertisements offered on this website are not intended for use by any person in any country or jurisdiction where such use would be contrary to local laws and regulations. The Products and Services offered on this website are not intended for residents of the United States, Malaysia and Thailand.
TMGM is authorized and regulated in various jurisdictions.
Trademax Australia Limited, trading as TMGM, is regulated by the Australian Securities and Investments Commission (ASIC), AFSL no. 436416 and is located at Level 28, One International Tower, 100 Barangaroo Avenue, 2000 Sydney, NSW Australia.
Email: support@tmgm.com.au
Trademax Global Limited, trading as TMGM, is authorized and regulated by the Vanuatu Financial Services Commission (VFSC), registration number 40356 and registered at 1276, Kumul Highway, Port Vila, Vanuatu, Republic of Vanuatu.
Email: support@tmgm.com
Trademax Global Markets (SE) Limited, trading as TMGM, is authorized and regulated by the Financial Services Authority (FSA) of Seychelles, with license number SD224. The company is registered at Office No 13, Providence Estate ABIS Centre, Mahe, Seychelles.
Email: support@tmgm.com
Trademax Global Markets (International) Pty Ltd, trading as TMGM, is authorized and regulated by the Financial Services Commission, Mauritius (FSC) with license no. GB22201012, and registered at 33, Edith Cavell Street C/o IQ EQ Fund Services (Mauritius) Ltd Port Louis, 11324 Mauritius.
Email: support@tmgm.com
Copyright © TMGM. All rights reserved